Coinone and Mega MGC Coffee have each said that an attacker reached their customer-support data by breaking into systems at MetaM, the contractor that runs those services for them.
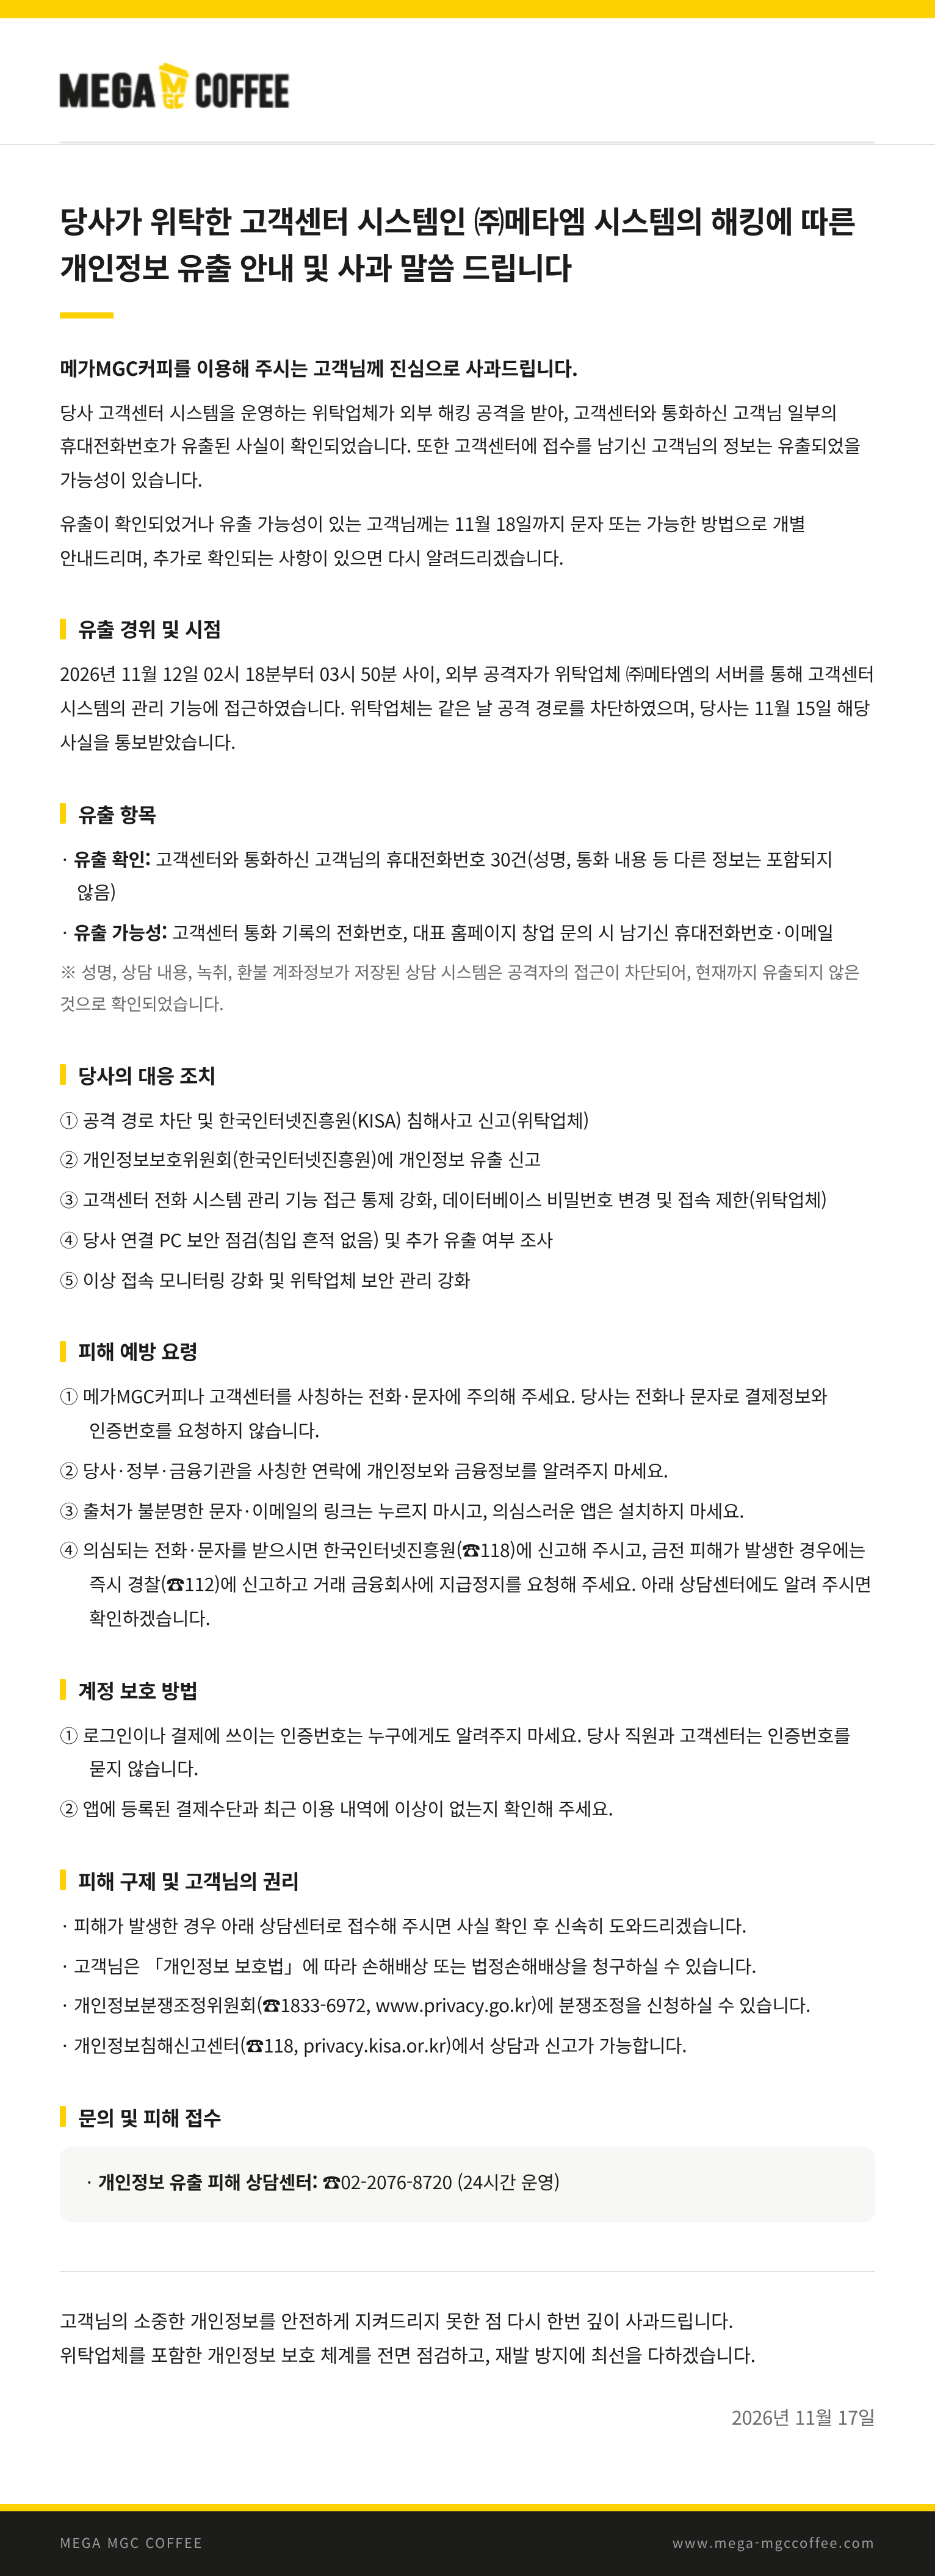
In a notice registered at 08:00 Korea time on 15 November (23:00 GMT on 14 November), the crypto exchange Coinone said an outside attacker unlawfully accessed the server of its support contractor, MetaM, at about 04:00 Korea time on 12 November (19:00 GMT on 11 November), and that it was told by MetaM at about 09:20 Korea time that day (00:20 GMT on 12 November). Mega MGC Coffee, in a homepage notice dated 17 November, gives a different window: it says an outside attacker accessed the management function of its customer-centre system through MetaM’s server between 02:18 and 03:50 Korea time on 12 November (17:18–18:50 GMT on 11 November), that MetaM blocked the route the same day, and that Mega was told on 15 November.
The two accounts describe the same contractor and the same date, but they should be kept as each company wrote them. Only Mega has given a confirmed headcount.
What Coinone and Mega MGC Coffee say MetaM exposed
Mega says it has confirmed the leak of mobile numbers of 30 customers who phoned its customer centre, and that names and other information were not included in that confirmed set. It says phone numbers in customer-centre call records, and emails left in start-up enquiries on its main website, may also have leaked. Names, consultation content, recordings and refund-account data have, according to the contractor, been confirmed not to have leaked so far. Mega says customers who were confirmed or may have been affected will be told individually by 18 November.
Coinone gives no number of affected people. It says customers who have no customer-centre consultation history are not involved, and that the information which may have leaked is what customers themselves left during chat or telephone support. The items it lists as possibly exposed are telephone number, name, email, date of birth, bank-account number, password, resident registration number, identity-document issue date, home address, wallet address and transaction ID (TXID). It stresses that this is a list of all fields that may have been involved, and that the items actually leaked can differ from person to person.
Coinone also says its member-account, trading and crypto-wallet systems are run separately from the contractor’s server, and that no sign of a direct intrusion into those systems has been found so far. Logins, it says, require two-factor authentication, and the leaked information alone cannot be used by a third party to log in to a customer’s account or withdraw assets. It has reported the incident to the Korea Internet and Security Agency (KISA), the Personal Information Protection Commission (PIPC) and the Financial Supervisory Service, blocked the internet addresses used in the attack and access to the customer centre, tightened monitoring, begun its own check of the contractor’s security, and switched the outsourced customer centre to email support.
Mega says the attack path has been blocked, that MetaM reported the matter to KISA, and that Mega has reported the leak to the PIPC. It also says it is auditing the customer-centre telephone system and its own network and website, and that no change, deletion or password reset of data has been confirmed so far.
Both companies warn customers about impersonation, phishing and unsolicited requests for passwords or payment details, and point them to official reporting channels. A contractor that holds support records for more than one client is a recurring path in recent disclosures. NTT Data has reported a subcontractor breach that exposed Japanese bond buyers’ details. In South Korea this autumn, Daishin said a hack exposed 38,490 customers as the authorities also probed Bithumb, and a wider wave was tied to 16 financial firms, including the operator of the crypto exchange Gopax. Those are separate cases. Nothing in the Coinone or Mega notices attributes this MetaM incident to the same actors, or says that any other MetaM client was hit.
Two clocks and one confirmed count are not the same account
The useful way to read these notices is to keep their measurements apart. Mega has confirmed 30 mobile numbers, for people who telephoned its customer centre, and has drawn a line around what it says has not, so far, been shown to have leaked. Coinone has given a wide list of support-data fields that may have been exposed, with no count, and has limited the group to people who used chat or phone support. Those are not interchangeable figures. A list of possible fields is not a finding that every field left every customer.
The attack times should be treated the same way. Coinone places the access at about 04:00 Korea time on 12 November. Mega places it between 02:18 and 03:50 that morning. Both can be reported as stated without forcing them into a single clock. The companies learned of the incident on different days, and only Mega has promised individual notices by a stated date, 18 November.
Coinone’s reassurance about trading and wallet systems also has a clear limit. The exchange says those systems are separate, that no direct intrusion has been found, and that the leaked support data alone is not enough to log in or withdraw assets. That is a statement about the trading platform, not a claim that a resident registration number, a bank-account number or a password left in a support chat is harmless. The outstanding questions are how far the MetaM access went, whether Coinone will later give a headcount, and whether any other MetaM client comes forward. On the two official notices now available, the incident is a contractor support-system breach that has hit an exchange and a coffee chain, and only those two clients have said they were involved.
How we sourced this
The account above is drawn from Coinone’s Korean-language notice, registered at 08:00 Korea time on 15 November 2026, and from Mega MGC Coffee’s Korean homepage pop-up notice dated 17 November 2026. Translations into English are by TSN. Times in the originals are Korea time; GMT equivalents are given in the article.
Sources
- Coinone, notice on a personal-information leak, registered 15 November 2026
- Mega MGC Coffee, homepage notice on a MetaM customer-centre leak, 17 November 2026
Get TSN’s biggest tech stories, explained.
News and insights across AI, tech, crypto and cybersecurity. Every source linked. Unsubscribe anytime.
Get the newsletterRelated stories
- Daishin Says Hack Exposed 38,490 Customers as Korea Probes Bithumb is the closest recent TSN file on a South Korean financial firm and a crypto-exchange investigation, and the right next stop for that domestic context.
- South Korea’s Financial Hacks Spread to 16 Firms, Including the Operator of Crypto Exchange Gopax; About 100,000 Records Presumed Leaked
- FBI Names North Korea in $6bn+ Binance Hack as Withdrawals Reopen in Phases
Follow @tsnmediahub on X for breaking AI news as it happens.
Follow on X